1. The Cloud Converter Trap: How Free Web Utilities Harvest Confidential JSON Payloads
Modern software engineering, data analytics, and operational reporting revolve around JSON (JavaScript Object Notation, RFC 8259). When querying REST APIs, microservices, CRM databases, or payment gateways like Stripe and PayPal, developers and analysts receive rich, structured JSON payloads. Yet business stakeholders, financial controllers, and marketing leads require these records formatted as tabular CSV spreadsheets for analysis in Microsoft Excel, Google Sheets, or business intelligence platforms.
To bridge this gap quickly, analysts frequently turn to search engines and paste raw data into "free online JSON to CSV converters." This seemingly benign operational shortcut constitutes one of the most widespread, unmonitored attack vectors in corporate environments today.
The Cloud Ingestion Architecture
Standard web converters operate on a server-side request-response cycle. When you click 'Convert', your entire JSON file travels across the open Internet via an HTTP POST request to an external server. The server writes your raw data into temporary disk caches, processes the conversion via Python or PHP, and streams back a file download.
Threat Level: Critical Data Exposure & Server-Side LoggingThe Client-Side Sandbox Architecture
Modern web browsers function as secure, isolated operating environments. Using native JavaScript engines (V8, SpiderMonkey) combined with the Web Streams API and Web Workers, data transformation occurs strictly within your machine's volatile RAM memory. No network packets leave your computer, rendering remote interception impossible.
Security Model: 100% Zero-Trust Local ProcessingConsider what typical production JSON payloads actually contain: customer personally identifiable information (PII) including full names, email addresses, phone numbers, and physical mailing coordinates; unhashed internal database record IDs; confidential billing schedules; proprietary pricing calculations; and even leaked API authorization tokens embedded in query parameters. Transmitting this information to an unvetted third-party converter violates fundamental corporate data governance and exposes organizations to catastrophic regulatory penalties.
Understanding the internal structure of client-side transformation demonstrates why local processing is not only vastly more secure, but also mathematically superior in execution speed and data fidelity.
2. Hierarchical Trees vs Flat Tables: The Mathematical Mechanics of JSON Flattening
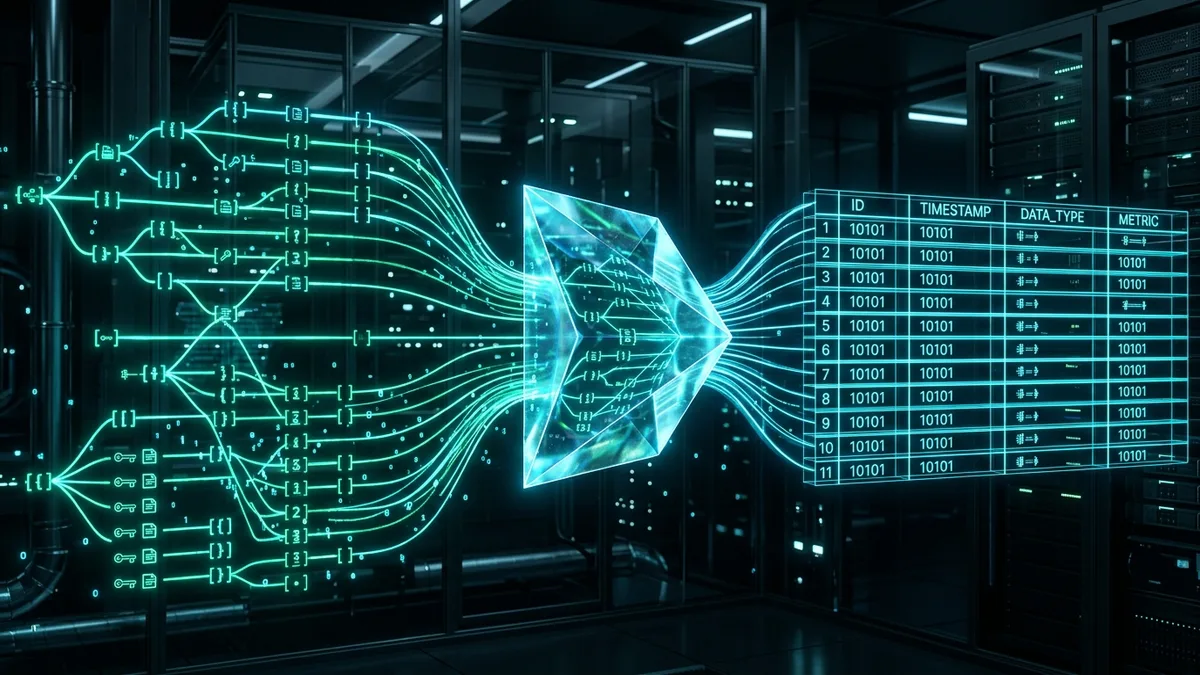
The fundamental technical challenge of converting JSON to CSV stems from a profound dimensional mismatch: JSON represents an n-dimensional hierarchical tree of arbitrary depth, while CSV represents a strictly two-dimensional matrix of fixed rows and columns.
A standard JSON record rarely consists of flat scalar values. Instead, it features deeply nested child objects, heterogeneous key structures, and variable-length arrays. Converting this structure cleanly requires an algorithmic flattening strategy:
parent_key.child_key.leaf_attribute = value
When an in-memory client-side parser traverses an object such as:
{
  "orderId": "ORD-9481",
  "customer": {
    "name": "Alex Mercer",
    "billingAddress": {
      "city": "Austin",
      "state": "TX",
      "postalCode": "78701"
    }
  },
  "tags": ["wholesale", "express-shipping"]
}
The recursive traversal algorithm unpacks the tree structure into a unified namespace:
orderId→"ORD-9481"customer.name→"Alex Mercer"customer.billingAddress.city→"Austin"customer.billingAddress.state→"TX"customer.billingAddress.postalCode→"78701"tags→"wholesale|express-shipping"(serialized delimiter array)
A critical challenge arises with heterogeneous schemas. In real-world API dumps, record #1 might possess fields A, B, and C, while record #2 introduces field D while omitting field B. Primitive converters crash or skew row alignments when encountering schema drift. A resilient client-side converter performs a preliminary key-collection pass across all records, building an exhaustive union set of all unique headers before generating the first row of CSV output, populating empty cells with null values seamlessly.
Convert JSON to CSV Locally in Browser Memory
Transform complex nested JSON data into RFC 4180 compliant CSV files with custom delimiters, dot-notation flattening, and UTF-8 BOM encoding—100% in your browser without uploading a single byte to external servers.
3. RFC 4180 Standards: Sanitizing Delimiters, Line Breaks, and UTF-8 BOMs
Generating a CSV spreadsheet is deceptively complex. Simply joining array values with commas (array.join(',')) results in corrupted files as soon as any text value contains an embedded comma, a newline, or quotation marks. To ensure universal compatibility across Microsoft Excel, Apple Numbers, LibreOffice, and SQL databases, client-side serializes must strictly implement IETF RFC 4180 specifications.
1. Embedded Delimiter Escaping
If a data field contains the active delimiter (such as a comma in standard CSV or a tab in TSV), the entire cell must be wrapped in double quotes. For example, Austin, TX must serialize as "Austin, TX" to prevent premature column splitting.
2. Quote Character Escaping
If a field contains a literal double quotation mark, RFC 4180 mandates that the quote be escaped by doubling it (prefixing an additional quote). A description like 24" Monitor must serialize as "24"" Monitor".
3. Multiline Record Handling
Customer comments or error logs often contain carriage returns (
) or line feeds (
). Enclosing the multi-line string in quotes ensures spreadsheet parsers treat the block as a single cell rather than spawning malformed rows.
The UTF-8 Byte Order Mark (BOM) Riddle in Excel
Have you ever opened a freshly converted CSV file in Microsoft Excel only to find international characters (such as German ä/ö/ü, French é/è, Spanish ñ, or Cyrillic and Turkish letters) replaced by nonsensical symbols like é or ?
This frustrating phenomenon occurs because Windows versions of Microsoft Excel default to the legacy Windows-1252 or ANSI codepage when opening plain text files, unless an explicit UTF-8 Byte Order Mark (BOM) is detected at the beginning of the file stream. A robust client-side converter automatically prepends the 3-byte hex sequence 0xEF, 0xBB, 0xBF before assembling the final file Blob:
// Injecting UTF-8 BOM into a browser Blob for flawless Excel rendering
const bom = new Uint8Array([0xEF, 0xBB, 0xBF]);
const csvBlob = new Blob([bom, csvString], { type: 'text/csv;charset=utf-8;' });
This simple 3-byte preamble guarantees that Excel immediately initializes its UTF-8 decoder, ensuring crystal-clear character rendering across all languages and operating systems.
4. In-Memory Streaming: How Web Workers and Streams API Prevent Tab Freezes
A common critique of client-side web utilities is that they choke on large datasets. If an engineer attempts to parse a 150MB JSON API dump containing 250,000 transaction objects using a naive JSON.parse() call on the browser's main thread, the entire webpage freezes. The browser UI locks up, animations stop, and Chrome eventually presents the dreaded "Page Unresponsive" dialog.
Modern web architectures solve this completely through asynchronous multi-threading and streaming pipelines:
Web Worker Background Threading
const worker = new Worker('json-parser-worker.js');
By offloading parsing logic to a dedicated background Web Worker, the main UI thread remains at a silky-smooth 60 frames per second. Users can continue interacting with the page, viewing real-time progress indicators, and canceling operations without browser friction.
Chunked Streams & Zero-Copy Buffers
file.stream().pipeThrough(new TextDecoderStream())
Rather than loading the entire 150MB file into memory at once, the Web Streams API processes incoming byte chunks sequentially. As each JSON object chunk is deserialized and flattened, the serialized CSV row is pushed directly to an output accumulator stream, keeping the resident memory footprint minimal.
For data professionals building larger enterprise workflows, the educational platform at aFolksDigital Developer Academy provides comprehensive architectural tutorials on building high-performance browser stream pipelines and client-side data filters.
5. Step-by-Step Practical Blueprint: Converting Sensitive API Payloads Locally
Follow this zero-trust operational workflow to transform confidential JSON files into production-grade CSV spreadsheets entirely within local memory:
Load Your Source File into Browser RAM
Drag and drop your .json or .jsonl (JSON Lines) file into the client-side tool or paste raw text into the input field. Notice that your browser does not initiate an upload progress bar; the file is read instantly into local memory via the HTML5 File API.
Configure Flattening and Delimiter Options
Choose how nested keys should be formatted (dot-notation user.address vs underscore user_address). Select your preferred field delimiter: standard comma (,), tab for TSV ( ), or semicolon (;) widely preferred in European spreadsheet locales.
Inspect Live Tabular Preview
Review the real-time preview table rendered in your browser. Verify that nested properties have populated the expected columns, array items are properly joined, and empty fields are gracefully represented by null spaces.
Execute Conversion via Local Web Worker
Click 'Convert to CSV'. The background worker parses the entire data stream, escapes all RFC 4180 special characters, and synthesizes the finalized text payload entirely within browser memory.
Save Directly to Disk via Blob URL
The browser generates a local object URL (blob:http...) and prompts your native file system save dialog. Once the file is written to your local drive, the memory pointer is immediately released via URL.revokeObjectURL().
6. Comprehensive Architectural Matrix: In-Browser vs Cloud SaaS vs CLI Utilities
The table below evaluates the three primary approaches to JSON-to-CSV transformation across data security, operational speed, schema resilience, and setup friction:
| Feature / Criteria | Client-Side In-Browser Tool | Cloud SaaS Web Converter | Command-Line Script (Python / jq) |
|---|---|---|---|
| Data Privacy & Leak Risk | Zero risk (100% in-browser RAM) | High (Server logging & transit leak) | Zero risk (Local OS execution) |
| Setup & Technical Barrier | Zero (Instant in any web browser) | Zero (Immediate web form) | Moderate (Requires Python, CLI env) |
| Nested Key Unpacking | Automatic recursive dot-notation | Often truncates or creates raw JSON cells | Custom coding required per schema |
| RFC 4180 Escaping | Built-in delimiter & quote escaping | Inconsistent across free tools | Supported via libraries (e.g. csv module) |
| Excel UTF-8 BOM Handling | Auto-injected 0xEF, 0xBB, 0xBF bytes | Rarely included (causes accent bugs) | Manual flag: utf-8-sig encoding |
| Cost & Subscription Friction | 100% Free & Unrestricted | Freemium caps, ads, $20/mo paywalls | 100% Free & Open Source |
7. Regulatory Compliance: GDPR, HIPAA, and Zero-Trust Data Pipeline Standards
Modern privacy regulations hold businesses accountable for every tool in their data supply chain. Under Article 28 of the European Union's General Data Protection Regulation (GDPR), transmitting customer data to an external processor requires an executed Data Processing Agreement (DPA) and rigorous security verification. Uploading a customer database export to a random web converter directly breaches GDPR compliance, triggering potential fines up to 20 million euros or 4% of worldwide annual turnover.
Similarly, under the Health Insurance Portability and Accountability Act (HIPAA) in the United States, exposing Protected Health Information (PHI) to cloud tools lacking Business Associate Agreements (BAAs) constitutes a reportable data breach. Under SOC 2 Type II compliance standards, unauthorized cloud data transmission invalidates organizational trust principles.
Client-side conversion circumvents these compliance bottlenecks entirely. Because data processing occurs strictly on the local hardware within the client's isolated application layer, no external data transfer takes place. Organizations can maintain strict zero-trust standards without compromising analyst productivity.
For organizations navigating complex digital governance frameworks, aFolksDigital Enterprise Consulting provides specialized guidance on implementing privacy-first architectures and compliant internal data utilities.
8. Frequently Asked Questions (FAQ)
Is it safe to convert JSON containing personal customer data using online converters?
Traditional online converters transmit your JSON payload to remote cloud servers where it is logged, cached, or analyzed by third parties, creating catastrophic GDPR, HIPAA, and CCPA violations. Safe conversion requires pure client-side processing in local browser memory where zero network requests occur.
How does client-side flattening handle deeply nested JSON objects and arrays?
Client-side parsers employ recursive flattening algorithms that concatenate nested object keys with dot-notation (e.g., user.address.zipcode) into distinct column headers, while array values are serialized into pipe-delimited strings or expanded into relational child rows.
Why do CSV files generated from JSON open with garbled special characters in Microsoft Excel?
Microsoft Excel defaults to legacy ANSI encoding unless a file contains an explicit UTF-8 Byte Order Mark (BOM). Client-side converters prepend the 3-byte sequence (0xEF, 0xBB, 0xBF) to the CSV text stream, ensuring Excel renders international accents, non-Latin scripts, and symbols flawlessly.
Can browser-based converters handle 100MB+ JSON files without freezing the tab?
Yes, by offloading JSON tokenization and CSV serialization to dedicated background Web Workers and utilizing chunked FileReader streams. This keeps the browser main execution thread completely free and prevents tab crashes or unresponsive UI warnings.
What formatting rules must a CSV file follow under RFC 4180 standards?
Under IETF RFC 4180, fields containing commas, line breaks, or double quotes must be enclosed in double quotation marks. Any literal double quote within a field must be escaped by prefixing it with another double quote (e.g., ""quoted"").
Related Guides in Developer Utilities & Data Security
Verify SHA-256 Checksum Offline
Verify cryptographic file integrity in browser memory using the native Web Crypto API.
GuideStatic vs Dynamic QR Codes: Security Risks
Examine redirection vulnerabilities, quishing attacks, and privacy-preserving QR generation.
GuideFlatten PDF Form Fields Offline
Lock interactive AcroForms into immutable vector page streams without cloud processing.