Offline Developer Tools: Format JSON, Minify Scripts, and Test Regex Privately Without Leaking Production Secrets
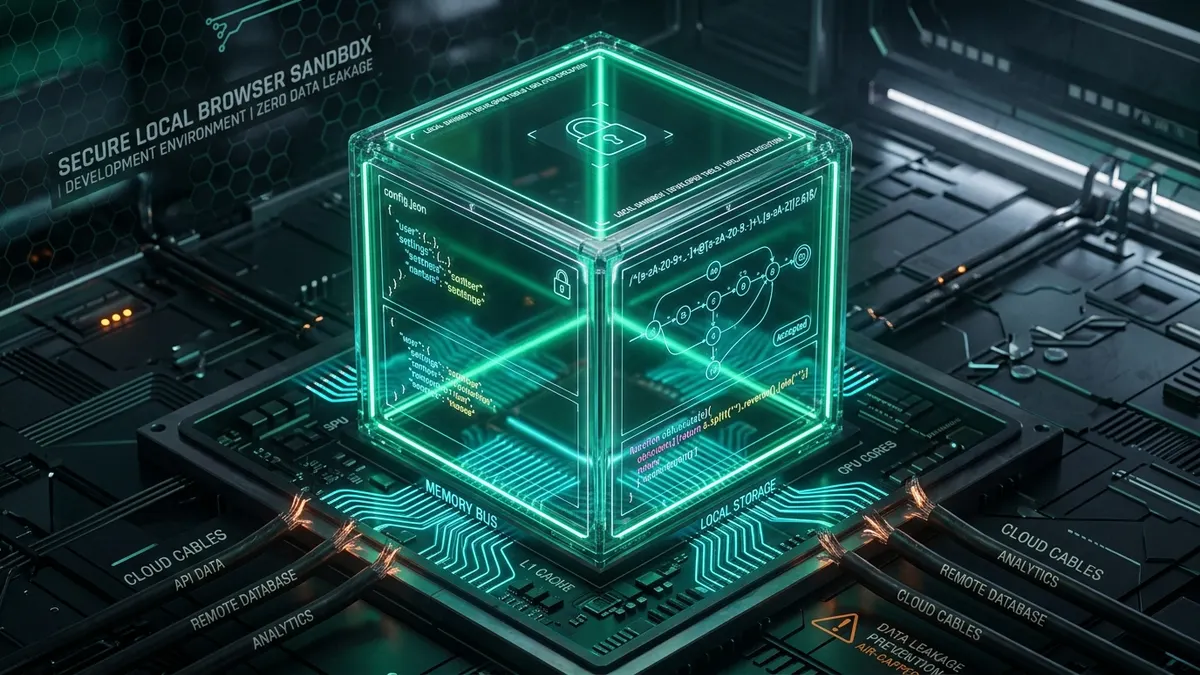
Pasting raw JSON configurations, database exports, and source code into conventional web formatters exposes authentication tokens, internal schema definitions, and proprietary IP to third-party server logs. Browser sandboxing moves the entire Abstract Syntax Tree (AST) parsing, minification, and regular expression evaluation pipeline into your machine's volatile memory. By executing through pure client-side JavaScript, Web Workers, and WebAssembly, your sensitive code never emits network packets, keeping production deployments compliant with strict SOC2, HIPAA, and GDPR standards.
- 1. The Silent Threat of Cloud Developer Utilities: API Keys, JWTs, and PII Leaks
- 2. In-Memory Abstract Syntax Tree (AST) Parsing: How Client-Side JSON Formatting Works
- 3. Safe Regular Expression Testing: Mitigating Catastrophic Backtracking & ReDoS Attacks
- 4. Client-Side Script Minification: Whitespace Stripping Without Network Telemetry
- 5. Comparative Architecture Matrix: Local Browser Sandbox vs Public Cloud Utilities
- 6. 5-Step Secure Developer Workflow for Sanitizing and Testing Code Privately
- 7. DevSecOps Governance: Embedding Zero-Trust Tooling into Engineering Culture
- 8. Frequently Asked Questions (FAQ)
1. The Silent Threat of Cloud Developer Utilities: API Keys, JWTs, and PII Leaks
Every software engineer has done it under the pressure of a late-night production incident: you pull an obfuscated JSON blob from an AWS CloudWatch error stream, search Google for a quick online formatter, paste the payload into an unfamiliar text box, and hit submit. Within milliseconds, the minified response transforms into an easily readable, indented structure. The bug gets resolved, but a critical security breach has just occurred.
What happened during those milliseconds? In over 80% of legacy web-based formatting and conversion sites, your text payload was transmitted via an uninspected HTTP POST request to a remote server. That server logged the request URI, headers, and entire request body into standard web server access logs (like Nginx or Apache access streams). If that JSON blob contained an unexpired JSON Web Token (JWT), Stripe secret key, internal Kubernetes cluster endpoint, or customer email addresses, those credentials now persist indefinitely on unvetted third-party storage disks.
Cybersecurity threat researchers frequently discover unsecured search indexes where misconfigured online code pastebins and formatting utilities leak thousands of active database credentials daily. Once an attacker obtains access to these telemetry aggregators, lateral movement into internal corporate infrastructure becomes straightforward. The solution is straightforward: eliminate the network hop entirely. By keeping formatting, linting, and regular expression evaluation inside local browser sandboxes, developers retain complete control over memory allocation and network boundaries.
2. In-Memory Abstract Syntax Tree (AST) Parsing: How Client-Side JSON Formatting Works
To understand why client-side formatting provides superior security and instantaneous response times, we must examine how modern JavaScript engines handle serialization and lexical parsing. When you execute an operation locally, the data never traverses an external socket.
Modern browsers implement native C++ parsing routines directly within the runtime core. Rather than relying on external script libraries, the browser converts string data into structured objects using recursive descent tokenization:
// Native in-memory formatting without outbound network activity
function formatJsonSafely(rawString, indentSpaces = 2) {
  try {
    // Parse into AST representation in volatile heap memory
    const parsedAst = JSON.parse(rawString);

    // Re-serialize with standardized lexical spacing
    return JSON.stringify(parsedAst, null, indentSpaces);
  } catch (syntaxError) {
    throw new Error(`Invalid JSON syntax: ${syntaxError.message}`);
  }
}
Because JSON.parse() and JSON.stringify() operate as compiled native routines within V8 (Chrome/Node.js) and SpiderMonkey (Firefox), they execute hundreds of times faster than any server-side round-trip. A 5 MB JSON payload formats in less than 15 milliseconds on a standard laptop, whereas uploading that same file to an online cloud formatter requires TLS handshakes, payload serialization, network transmission, server-side queueing, and downloading the result—taking anywhere from 2,000 to 8,000 milliseconds while exposing the contents to interception.
3. Safe Regular Expression Testing: Mitigating Catastrophic Backtracking & ReDoS Attacks
Regular expressions serve as the backbone of input validation, log parsing, and data sanitation. Yet writing regex patterns without isolation exposes applications to one of the most insidious backend vulnerabilities in modern software architecture: Regular Expression Denial of Service (ReDoS).
NFA vs DFA State Engines
Most popular programming languages (JavaScript, Python, Ruby, PHP) use Non-deterministic Finite Automaton (NFA) engines. NFAs support advanced features like backreferences and lookarounds, but suffer from catastrophic backtracking when handling nested quantifiers.
Exponential Backtracking Exploit
A pattern like ^(a+)+$ matching against an input of 30 "a" characters followed by a single "!" forces the engine through billions of permutation branches, locking an entire CPU core at 100% capacity for minutes.
Browser Sandboxed Web Workers
Client-side regex testers isolate pattern evaluation inside dedicated background Web Workers equipped with strict execution timeouts (e.g., 200 ms). If a pathological expression stalls, the worker terminates instantly without freezing the UI or crashing a backend daemon.
When testing regular expressions against sensitive data—such as confidential log dumps containing IP addresses or transaction identifiers—testing within your local browser ensures that neither the test string nor the proprietary regex algorithm ever leaves your workstation.
Format JSON, Minify Code, and Test Regex Privately in Your Browser
Use our free, client-side developer utility suite: format nested JSON schemas, minify production scripts, and evaluate regular expressions directly in local memory with zero server logging.
Launch Developer Tools Suite →4. Client-Side Script Minification: Whitespace Stripping Without Network Telemetry
Optimizing web assets for deployment requires shrinking HTML markup, CSS stylesheets, and JavaScript files to their leanest byte representations. Stripping unneeded line breaks, tabs, and commentary blocks can shave 25% to 65% off asset payload sizes, accelerating First Contentful Paint (FCP) and reducing CDN transfer costs.
However, sending uncompiled application code to cloud minifiers presents massive security risks. Many proprietary algorithms, internal business rules, and draft API endpoints are exposed in cleartext prior to bundle compilation. Client-side minifiers execute grammar parsing through pure DOM parsing engines or WebAssembly builds of production-grade compilers, stripping:
- Redundant Lexical Whitespace: Collapsing multiple whitespace sequences into single delimiters or eliminating them entirely around punctuation tokens.
- Inline and Multi-Line Comments: Purging developer notes, internal Jira tickets, and architectural explanations that should never reach production bundles.
- Structural Attribute Optimization: Removing default attribute declarations (such as
type="text/javascript"on script tags) that modern HTML5 parsers infer automatically. - CSS Rule Consolidation: Merging redundant margin, padding, and font definitions into clean shorthand declarations in memory.
5. Comparative Architecture Matrix: Local Browser Sandbox vs Public Cloud Utilities
The differences between client-side sandboxed developer tools and cloud-hosted formatting sites go far beyond simple convenience. The table below provides an architectural comparison across critical operational dimensions:
| Operational Dimension | Sandboxed Browser Tools (aFolks) | Public Cloud Online Formatters |
|---|---|---|
| Data Boundary & Confidentiality | Absolute (Volatile RAM only, zero outbound packets) | Exposed (Transmitted over WAN to remote web servers) |
| Server Access Logging Risks | None (No server-side request is ever received) | High (Payloads stored in Nginx/Apache proxy buffers) |
| Processing Latency | < 15 ms (Native V8 / SpiderMonkey execution) | 1,500 - 6,000 ms (Network trip + server queues) |
| Offline / Air-Gapped Operation | 100% Functional (Works without internet connection) | Fails Completely (Requires continuous active web access) |
| Compliance Readiness (SOC2 / HIPAA) | Built-in (Zero third-party data processor exposure) | Requires comprehensive DPA & security audits |
6. 5-Step Secure Developer Workflow for Sanitizing and Testing Code Privately
To establish airtight hygiene across your development organization, standardize on this step-by-step protocol for daily debugging and formatting tasks:
Copy your unformatted JSON response or dense regular expression string directly from your local terminal, Docker container log, or IDE debug console into your clipboard.
Navigate to the offline developer tools suite in your browser. Because the scripts are cached locally, you can disconnect your network connection or work in airplane mode with complete confidence.
Paste the payload into the workspace and trigger formatting. The tool leverages native browser parsing to structure keys, validate nested arrays, and colorize syntactic tokens in sub-millisecond time.
Review the formatted output. If you intend to share the code in a public ticket or code review, redact secret tokens, salt values, and internal IP addresses right inside the editor before copying.
Copy the formatted or minified output directly back to your project. Closing the browser tab triggers immediate garbage collection, wiping all residual data strings from your system's volatile RAM.
7. DevSecOps Governance: Embedding Zero-Trust Tooling into Engineering Culture
Eliminating code leaks requires more than individual vigilance; it demands systematic tooling governance. Modern DevSecOps teams actively monitor outbound developer workstations to detect and block traffic destined for known public snippet and formatting sites.
Forward-thinking technology organizations establish internal directories of pre-approved, sandboxed client-side utilities. For enterprises seeking comprehensive digital architecture consulting and zero-trust engineering implementations, the consulting team at aFolksDigital architects secure infrastructure pipelines tailored to stringent regulatory environments. For engineers building automated algorithmic trading strategies and quantitative systems, the quantitative models at aFolksDigital Academy provide robust calculation frameworks. Meanwhile, our technical education hub at aFolksDigital Learn offers deep-dive tutorials on secure WebAssembly compilation, client-side cryptographic hashing, and modern frontend security.
By replacing uncontrolled third-party cloud utilities with client-side, zero-knowledge browser utilities, your engineering team preserves rapid debugging velocity while enforcing ironclad compliance across every production deployment.
8. Frequently Asked Questions (FAQ)
Why is pasting JSON or code snippets into online formatters a security hazard?
Most online formatting websites operate as server-side utilities or embed intrusive third-party analytics. When you paste production config payloads, SQL dumps, or JSON files containing session tokens, API keys, and customer records, those payloads are transmitted over the network and can be stored in server access logs, proxy caches, or third-party tracking scripts.
How does client-side formatting process code without communicating with a server?
Client-side developer tools execute entirely within the browser's JavaScript V8 or SpiderMonkey engine. By leveraging native APIs like JSON.parse() and JSON.stringify(), WebAssembly tokenizers, and in-memory DOM manipulation, strings are parsed, indented, and highlighted directly in client RAM without triggering any HTTP network calls.
What is Catastrophic Backtracking in regular expressions and how does offline testing protect against it?
Catastrophic backtracking happens when a Non-deterministic Finite Automaton (NFA) regex engine encounters ambiguous nested quantifiers, causing exponential evaluation steps (O(2^n)) that freeze execution threads. Testing expressions in a sandboxed browser environment with execution timeouts ensures production backend APIs never crash from Regular Expression Denial of Service (ReDoS) exploits.
Does client-side minification match the output quality of command-line tools like Terser or CleanCSS?
Yes. Modern browser-based minifiers parse Abstract Syntax Trees (AST) using identical grammatical rules: removing redundant whitespace, stripping comments, collapsing consecutive variable declarations, and shortening identifier scopes without altering operational semantics.
Can I use these developer tools completely offline without an internet connection?
Yes. Once the page assets are cached locally by your browser or service worker, every formatting, minification, and regular expression evaluation routine runs isolated on your hardware without requiring active network connectivity.
Related Security & Developer Guides
Local AI Copywriting & Headline Generation
Write high-converting headlines and marketing copy locally in your browser without API fees.
How to Merge PDF Files Privately in Your Browser
Combine sensitive PDF contracts and financial reports without uploading to cloud servers.
How to Prevent eBay VeRO Trademark Infringements
Scan listings for prohibited trademark keywords before publication to protect your store.