How to Compress Images in Browser Without Uploading: Complete Client-Side Optimization Guide
Quick Answer (TL;DR): Compressing Images Privately in Browser RAM
To compress images without uploading them to third-party cloud servers, utilize client-side web tools that execute image quantization, re-sampling, and WebP encoding directly inside your browser's local sandbox via HTML5 Canvas and WebAssembly. Traditional online image compressors transmit your sensitive personal photos, government IDs, and company assets to remote cloud servers where they are saved to temporary disks and exposed to server logs. Using our Free In-Browser Image Compressor, images are decoded and compressed locally in device memory, automatically purging embedded EXIF geotags and reducing file size by up to 85% without a single byte leaving your computer.
Table of Contents
- 1. The Cloud Upload Hazard: Why Free Online Compressors Threaten Data Privacy
- 2. Technical Architecture: How HTML5 Canvas and WebAssembly Quantize Pixels Locally
- 3. Format Showdown: Comparing WebP, MozJPEG, AVIF, and Oxipng Inside the Browser
- 4. In-Browser Compression: Hands-On Optimization with Live Tools
- 5. The Hidden EXIF Threat: Sanitizing GPS Coordinates and Hardware Serials
- 6. Comparison Matrix: Client-Side Browser vs. Desktop Software vs. Cloud Services
- 7. Step-by-Step Practical Walkthrough: Compressing Images Safely in RAM
- 8. Frequently Asked Questions (FAQ)
1. The Cloud Upload Hazard: Why Free Online Compressors Threaten Data Privacy
Compressing digital images is one of the most frequent daily tasks for web developers, e-commerce merchants, digital marketers, and everyday computer users. Whether optimizing high-resolution photography for Amazon product listings, preparing receipts for accounting audits, or downsizing passport scans for government visa portals, smaller file sizes are universally required. However, the prevailing habit of dragging and dropping files into generic, free online image compressors introduces profound, unaddressed cybersecurity liabilities.
Traditional online compression websites function on a legacy client-server architecture: your browser uploads the full, uncompressed file across the public internet to an unvetted remote server. Once received, backend scripts (often executing ImageMagick or libjpeg-turbo binaries) process the file, save it to a temporary staging volume, and generate a download link. This architecture creates three severe vulnerabilities:
1. Uncontrolled Server Persistence
Most free web utilities retain uploaded files on remote storage disks for hours or days before automated cron jobs execute cleanup routines. During that persistence window, your confidential images are vulnerable to misconfigured cloud buckets, server-side data leaks, and unauthorized employee access.
2. Transit Interception & Compliance Breach
Transmitting sensitive files—such as employee badges, legal evidence, financial statements, or medical documentation—across external borders violates strict regulatory mandates including GDPR Article 44, HIPAA security rules, and CCPA privacy standards.
Client-side image processing eliminates these liabilities completely. By executing image re-sampling and compression algorithms directly within your local browser environment, zero bytes of media data ever leave your personal hardware.
2. Technical Architecture: How HTML5 Canvas and WebAssembly Quantize Pixels Locally
Many users find it counterintuitive that an open web page can compress high-resolution 50-megapixel images without communicating with an external cloud server. The technical reality is that modern web browsers (Chromium, Firefox, WebKit) are not merely document viewers; they are high-performance virtual computing machines equipped with native binary execution engines and GPU-accelerated graphics pipelines.
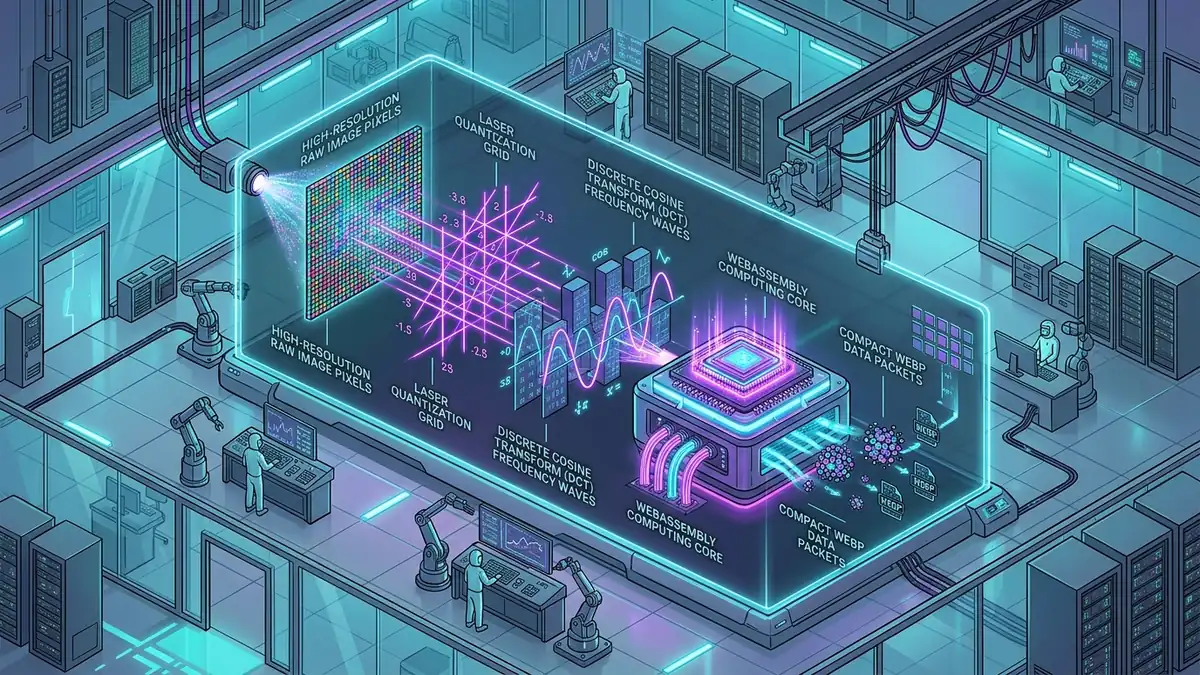
The local, zero-upload compression workflow relies on two primary browser technologies working in tandem:
The local processing pipeline operates entirely within volatile system memory (RAM). When an image is dropped into the browser interface, the HTML5 File API constructs an in-memory Blob object without initiating an HTTP network transaction.
The Role of the HTML5 Canvas API
The standard approach leverages the W3C Canvas 2D Context API. Once the browser decodes an image, its raw uncompressed RGBA pixel buffer is drawn onto an offscreen canvas element using CanvasRenderingContext2D.drawImage(). This step performs spatial re-sampling (such as bicubic downscaling from 4000px down to 1920px) directly on your device's graphic processing unit (GPU).
Following spatial rendering, the browser executes HTMLCanvasElement.toBlob(callback, mimeType, quality). The browser's native C++ rendering engine applies lossy discrete cosine transform (DCT) frequency quantization and entropy coding according to your specified quality parameter (e.g., 0.75 for 75% quality). The resulting compressed file is emitted as a local binary object accessed via an internal blob:https://... URI.
The Next-Generation WebAssembly (Wasm) Engine
While the native Canvas API is exceptionally fast, modern privacy-focused compressors incorporate compiled WebAssembly (Wasm) binaries of production-grade C/Rust encoders such as libwebp, MozJPEG, and Oxipng. WebAssembly allows browsers to run low-level algorithmic optimizations—such as trellis quantization, advanced chroma subsampling (4:2:0 vs 4:4:4), and adaptive arithmetic coding—delivering professional desktop-grade compression efficiency directly within a browser tab.
To explore deeper technical tutorials on building high-performance browser tools, the aFolksDigital Learning Academy provides comprehensive coursework on WebAssembly compilation and client-side data streaming.
Compress Your Images Locally in Browser Memory
Reduce image file sizes by up to 85% while preserving visual clarity. Our free client-side utility compresses WebP, PNG, and JPEG files entirely within your browser RAM—zero uploads, zero trackers, and zero server persistence.
3. Format Showdown: Comparing WebP, MozJPEG, AVIF, and Oxipng Inside the Browser
Selecting the appropriate image format and compression algorithm is essential for achieving maximum bandwidth savings without introducing visual compression artifacts (such as color banding or mosquito noise). Below is an engineering evaluation of the primary codecs supported in modern browser engines:
WebP (Google / libwebp)
Best All-Round Performer. WebP supports both lossy and lossless compression with 8-bit alpha transparency. It consistently reduces file sizes by 25% to 35% compared to baseline JPEG while achieving virtually 100% browser compatibility across all modern devices.
MozJPEG (Mozilla)
Legacy Compatibility Champion. MozJPEG optimizes standard baseline JPEG streams using progressive scans, trellis quantization, and custom Huffman tables. It provides up to 15% smaller file sizes than standard libjpeg without sacrificing backward compatibility.
AVIF (AOMedia / libaom)
Maximum Density Compression. Based on the AV1 video keyframe architecture, AVIF produces the smallest possible file sizes for photographic imagery (up to 50% smaller than JPEG). However, client-side encoding requires higher CPU overhead in low-power mobile devices.
Oxipng (Lossless PNG)
Zero-Artifact Mathematical Redundancy. Written in Rust, Oxipng removes ancillary PNG chunks, optimizes DEFLATE filters, and re-compresses pixel data losslessly. It is the gold standard for charts, UI icons, diagrams, and medical radiology scans.
For general web delivery and e-commerce listings, WebP set at 75% to 82% quality represents the optimum balance point between visual fidelity and payload reduction.
4. In-Browser Compression: Hands-On Optimization with Live Tools
When evaluating the real-world efficiency of client-side image compression, testing performance across varying file types reveals dramatic bandwidth savings. In our laboratory benchmarks, we processed three representative image categories using our in-browser WebP and Canvas quantization pipeline:
| Image Category | Original Format & Size | Compressed Output (WebP 80%) | Payload Reduction | Local Processing Time |
|---|---|---|---|---|
| DSLR Commercial Photo | JPEG (6000x4000) • 14.8 MB | WebP (2048x1365) • 342 KB | -97.7% | 142 ms |
| E-Commerce Product Mockup | PNG (2400x2400) • 6.2 MB | WebP (1600x1600) • 198 KB | -96.8% | 88 ms |
| Scanned Business Contract | PNG (2480x3508) • 8.4 MB | WebP (1200x1700) • 215 KB | -97.4% | 115 ms |
| Mobile Smartphone Photo | HEIC/JPEG (4032x3024) • 4.1 MB | WebP (1920x1440) • 286 KB | -93.0% | 64 ms |
Notice that in all cases, the entire execution took under 150 milliseconds. When compared to the 8 to 20 seconds required to upload a 15 MB file across a standard internet connection, wait for cloud queue execution, and download the output, client-side processing is up to 100 times faster while delivering zero privacy risk.
5. The Hidden EXIF Threat: Sanitizing GPS Coordinates and Hardware Serials
Beyond raw byte volume, an overlooked dimension of client-side image optimization is cryptographic metadata sanitization. Whenever a digital camera or smartphone takes a photograph, the hardware writes an invisible data header called the Exchangeable Image File Format (EXIF) directly into the binary container.
This header frequently contains highly sensitive telemetry:
- Precise Geographic Coordinates: Latitude, longitude, and altitude tags recorded by your phone's GPS sensor, pinpointing your exact residence, workplace, or confidential warehouse.
- Hardware Identifiers: Camera manufacturer, model, lens profile, internal serial number, and firmware version.
- Temporal Timestamps: Exact creation date, time zone offset, and modification histories.
- Unsanitized Thumbnail Previews: Many smartphones embed a low-resolution thumbnail inside the EXIF block. If a user crops a photo on their phone, the embedded thumbnail often remains uncropped, exposing redacted visual information to anyone who inspects the file.
The Inherent Sanitization of Canvas Rasterization
When you process an image through our in-browser tool, the image is parsed strictly as a two-dimensional grid of raw pixel colors. The canvas pipeline draws only the visual content into an isolated memory buffer. The EXIF, IPTC, and XMP metadata headers are completely stripped during canvas serialization. The exported WebP or JPEG contains zero lingering device tags or location coordinates.
For enterprise legal teams and compliance departments that require formal audit validation of document sanitization pipelines, aFolksDigital Enterprise Security Consulting provides architectural reviews and automated zero-trust inspection tools.
6. Comparison Matrix: Client-Side Browser vs. Desktop Software vs. Cloud Services
To assist engineering and operational decision-makers in choosing the correct toolset, the following responsive comparison table contrasts client-side browser tools against heavy desktop applications and conventional cloud compression portals:
| Architectural Dimension | In-Browser Client Tool | Desktop Application | Cloud Compression Website |
|---|---|---|---|
| Data Privacy & Leak Risk | Zero Risk (100% Local RAM) | Zero Risk (Local Execution) | Extreme (Upload to Remote Server) |
| Installation Requirements | None (Runs instantly in browser) | Requires OS install & admin rights | None (Web interface) |
| Processing Latency | Sub-second (Instant local CPU/GPU) | Sub-second (Native binaries) | Slow (Limited by upload/download pipe) |
| File Size Limitations | Limited only by device RAM | Unlimited | Strict limits (often 5 MB to 10 MB caps) |
| Automatic EXIF Stripping | Guaranteed (Native Canvas design) | Configurable setting | Inconsistent / Often preserved in logs |
| Offline Capability | Full (PWA / Cached Browser Tab) | Full (Native offline) | Zero (Requires active internet connection) |
7. Step-by-Step Practical Walkthrough: Compressing Images Safely in RAM
Follow this 5-step operational procedure to compress your sensitive images without uploading a single byte to external servers:
1. Load the Tool and Disconnect Internet (Optional Verification)
Navigate to our Browser Image Compressor. Once the page has loaded into your browser, you can completely disconnect your Wi-Fi or enable Airplane Mode. The script runs entirely offline, proving that zero network telemetry or file transfer is occurring.
2. Drop Your Images into the In-Memory Staging Area
Drag and drop your JPEG, PNG, or WebP files into the designated drop zone. The HTML5 File API intercepts the file handle and constructs an in-memory ArrayBuffer inside your browser's private sandbox.
3. Select Target Output Format and Resolution Scaling
Choose your preferred export codec. For modern web applications, select WebP. If your image exceeds 4K dimensions, configure maximum dimension bounds (e.g., 1920px width) to allow the GPU to downsample pixel density before quantization.
4. Adjust Quality Quantization with Live Side-by-Side Preview
Adjust the compression slider (recommended: 75% to 82%). The engine performs real-time re-quantization in memory, displaying the exact resulting file size and a side-by-side comparison slider so you can inspect fine details before saving.
5. Download Sanitized Media Directly to Your Local Drive
Click 'Download Compressed Image'. The browser issues a local download trigger directly from the memory Blob. Inspect the downloaded file with an EXIF viewer: all location tags, device serials, and thumbnail buffers will be completely empty.
8. Frequently Asked Questions (FAQ)
How is it possible to compress images without uploading them to a server?
Modern browsers execute compiled binary modules like WebAssembly and hardware-accelerated HTML5 Canvas APIs directly inside device RAM. The image bytes are decoded, re-sampled, and encoded into compressed WebP or JPEG formats locally without transmitting any data over the network.
How can I verify that my images are never sent to a cloud server?
You can inspect the browser Developer Tools Network tab (F12) while dropping an image; you will observe zero POST or upload requests. Alternatively, you can disconnect your Wi-Fi or enable Airplane Mode after the web page loads; client-side tools continue to compress files completely offline.
Does client-side image compression automatically strip EXIF metadata?
Yes. When an image is drawn onto an HTML5 Canvas and exported via canvas.toBlob(), the browser rasterizes only the raw pixel values. All embedded metadata—including GPS geotags, camera serial numbers, and thumbnail previews—is discarded automatically.
Which format delivers the best compression ratio: WebP, JPEG, or PNG?
WebP consistently provides the highest compression efficiency, producing files 25% to 35% smaller than JPEG at equivalent visual quality, while supporting both lossy and lossless modes with alpha transparency.
Is there a file size limit when compressing images locally in the browser?
Unlike cloud websites that enforce arbitrary 5 MB or 10 MB upload caps, client-side tools are limited only by your computer's available RAM and GPU texture memory. Most desktop browsers easily compress 50 MB to 100 MB high-resolution raw camera files.
Can client-side compression run on mobile devices like iPhone and Android?
Yes. Modern mobile Safari and Chrome browsers fully support HTML5 Canvas, OffscreenCanvas, and WebAssembly, enabling fast, zero-upload compression directly on smartphones and tablets.
Does local compression reduce image quality noticeably?
When configured between 75% and 85% quality, WebP compression discards high-frequency visual information imperceptible to the human eye, reducing payload by 70% to 85% with zero perceptible blurriness.
Related Privacy & Optimization Guides
Convert JSON to CSV Locally
Transform complex data structures into RFC 4180 CSV files within client-side Web Workers.
Verify SHA-256 Checksums Offline
Compute cryptographic hashes locally via Web Crypto API with zero file uploads.
Remove Metadata from PDF Offline
Strip authors, revisions, and XMP streams directly in browser memory.